What is DORA?
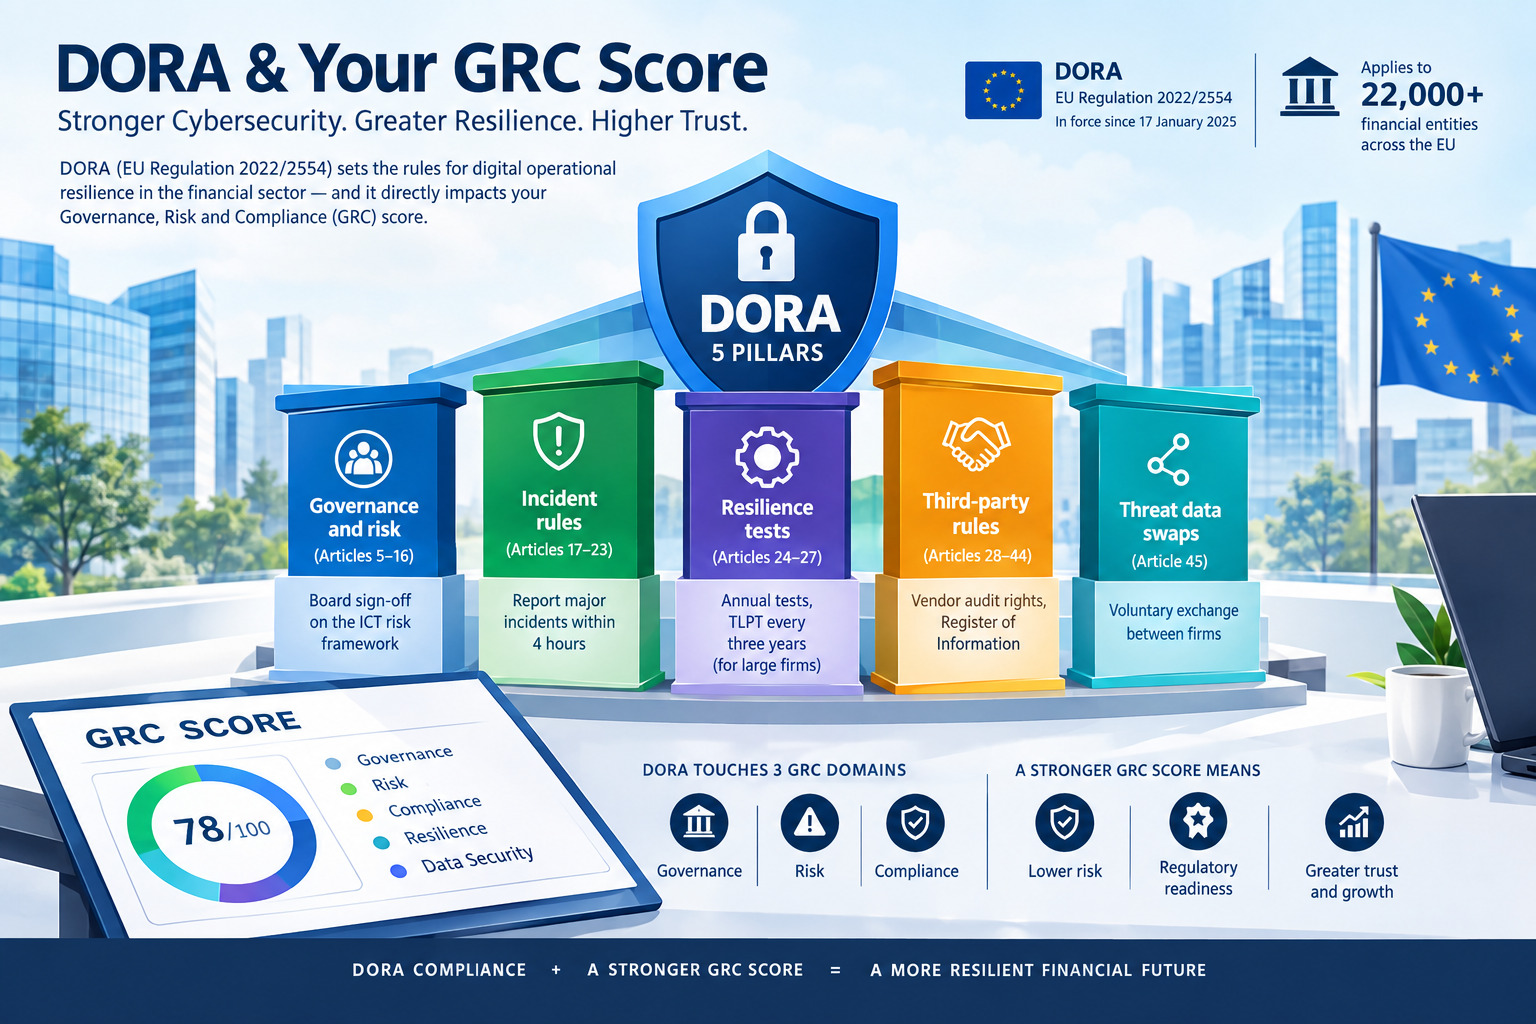
DORA stands for the Digital Operational Resilience Act. It is EU Regulation 2022/2554. The rule has applied to financial firms since 17 January 2025. It gives the financial sector and its key technology suppliers the same rules for cybersecurity and information technology (IT) security.
Over 22,000 financial entities sit inside its scope across the EU. National regulators began active checks the same month the rule took effect. Every firm inside scope must prove its systems survive a cyberattack or a system failure. A claim on paper no longer satisfies a regulator.
What Is DORA and Why Should Your GRC Score Care?
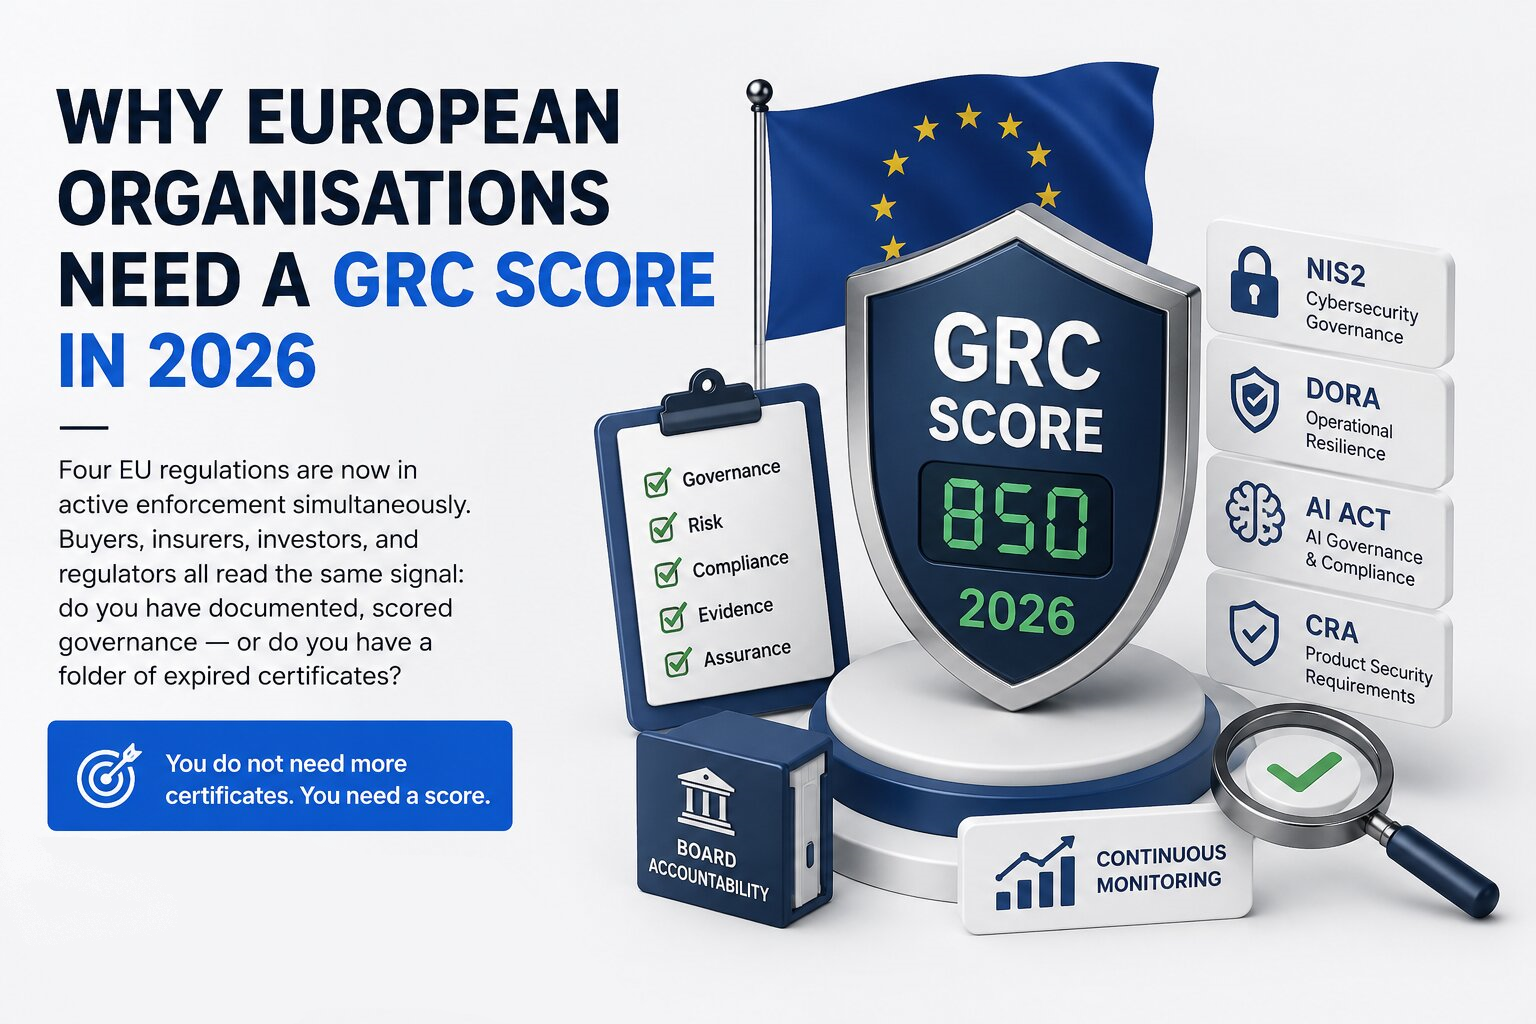
Your GRC Score already tracks governance, risk, and compliance across five domains. DORA sits inside three of those domains at once. A single gap rarely stays contained to one area.
A missing vendor clause can drag down your compliance score. The same gap often drags down your resilience score too. Your regulator never separates the two. Your rating should not either.
The 5 Pillars of DORA Compliance
DORA rests on five pillars. Each one carries its own article range and its own set of obligations.
Small firms face lighter versions of most rules. Article 4 sets out that proportional treatment. None of the five pillars sits fully optional though.
What Does a GRC Score Actually Measure at a Financial Firm?
A GRC Score rates your firm across five domains. Governance covers board oversight and policy. Risk management covers how you spot and control threats. Compliance covers your regulatory map and audit proof. Resilience covers your recovery plans and your test record. Data security covers your access controls and your encryption standard. The GRC Index benchmarks each domain against ISO 27001, SOC 2, and COSO. Over 1,100 organisations already hold a live score on that Index.
How Does Each DORA Pillar Feed Into a Different Part of Your Score?
Each DORA pillar lands on a different part of your GRC Score. The table below maps the link.
A weak vendor contract shows up twice on your record. It lowers your compliance score first. It lowers your risk score right after.
Which DORA Gaps Hit EU Financial Firms' Scores Hardest Right Now?
The main DORA compliance gaps that keep EU financial firms from being ready are the Register of Information (third-party contract mapping), advanced operational resilience testing, and supply chain risk management.
60% of companies say they have high-level ICT risk management governance, but only 7% of financial institutions surveyed say they are fully compliant across all components. This is based on market data and industry audits. Now that the initial enforcement grace period is over, national competent authorities (NCAs) such as BaFin in Germany and DNB in the Netherlands are carefully checking the following failure points. You can also check the recent gap review on the GRCI blog found the same three gaps across most 2026 assessments.
What Does a Falling GRC Score Cost You Beyond the Fine Itself?
A low GRC Score costs more than the fine on the page. Insurers use your score to price cyber cover. It triggers a chain reaction of reputational damage, operational and financial, that can destroy a business's long-term value.
Investors ask for your score during due diligence checks. A weak score slows deals down. Sometimes it kills a deal outright. Boards feel that pressure directly. Supervisors now interview directors on ICT risk directly. Credit rating agencies watch enforcement notices too. A public DORA notice can trigger a ratings review within weeks.
How Do You Turn DORA Compliance Into a Higher GRC Score?
To improve DORA Compliance and get Governance, Risk, and Compliance we need to switch from static, manual checklists to an ongoing, automatic assurance approach.
Send board members to an ICT update every year. A single update lifts your governance score fast. Also book your annual resilience test early. A late test leaves your resilience score exposed near year-end.
Structured courses on GRCI's course catalogue close the skill gaps behind a low score. Progress on all three points often lifts a score within one review cycle.
What Do EU Financial Firms Keep Asking About DORA and Their GRC Score?
The Digital Operational Resilience Act and how Governance, Risk, and Compliance (GRC) affect their business. With DORA being fully national, it is integrated directly into their daily monitoring.
Does DORA compliance guarantee a good GRC Score?
No, it does not. DORA covers ICT risk alone. Your GRC Score also weighs data security and general governance across the full firm.
How fast can a GRC Score move after a fix?
A (GRC) Score can move immediately, sometime within one minute to 24 hours. However, the exact time depends on how your company keeps track of compliance. Consumer credit scores are updated every 30 days, mostly based on evidence instead of time served.
Can a firm reach a top score without full DORA compliance?
A company cannot achieve a high score adhering of the DORA compliance. A top score needs full marks across all five domains. DORA gaps block resilience and compliance points on their own.
Do UK-only firms need to track DORA at all?
UK-only firms sit outside DORA's direct scope on paper. Firms that serve EU clients often fall inside scope anyway. The same applies to firms that supply EU financial firms.
Your GRC Score tells you exactly where you stand today. You should try the free GRC Score assessment. It gives you your own number within minutes.