SOC 2 vs ISO 27001: What Is the Difference?
Every business that handles customer data should need SOC 2 and iso 27001. Compliance standards are common practices for data safety. These 2 certificate and attestation report help companies build a strong and safe security system, which also helps customers to reduce their risk. Most people around the world use SOC 2 and ISO 27001 as their security certifications. In this article, we will explain both in detail and help you understand what SOC 2 is and what ISO 27001 is. How they can be beneficial for you, their differences, and how you can determine which is good for your business.
What Is SOC 2?
SOC 2 stands for System and Organization Controls 2. The American Institute of Certified Public Accountants (AICPA) created the framework for service organisations. It helps with the management and security of client data by service providers, including cloud service providers and SaaS (Software as a Service) suppliers.
SOC 2 has 5 trust service criteria. The five Trust Services Criteria include Security, Processing Integrity, Confidentiality, Availability and Privacy. Security is the only mandatory category because it protects data from damage and theft. You choose the other four to match your service. The AICPA says that SOC 2 is a report on controls that are linked to the five criteria. A licensed CPA firm tests your controls and issues an attestation report. SOC 2 is not a certificate. You receive an auditor’s opinion, not a pass mark. The report names each control, each test and each exception.
What Is ISO 27001?
The International Organization for Standardization (ISO), which is also known as IEC 27001 the International Electrotechnical Commission (IEC), publishes ISO/IEC 27001 as the international standard for information security. The standard sets rules for an information security management system, or ISMS. An ISMS is a set of policies, roles, risk checks and records. ISO states that the standard suits organisations of any size and sector.
You must comply with the standard’s clauses 4 to 10. They cover context, leadership, risk goals, support, operation, evaluation and improvement. Annex A then lists 93 controls in four themes. The themes are organisational, people, physical and technological.
The 2022 edition cut the list from 114 controls to 93, as BSI confirms. Every 2013 certificate expires after 31 October 2025. An approved certification organization verifies your ISMS and issues the certificate. UKAS accredits such bodies in the UK.
We also cover what ISO 27001 is and the ISMS in more depth. It also explains the mandatory records and the audit steps.
SOC 2 vs ISO 27001: The Difference
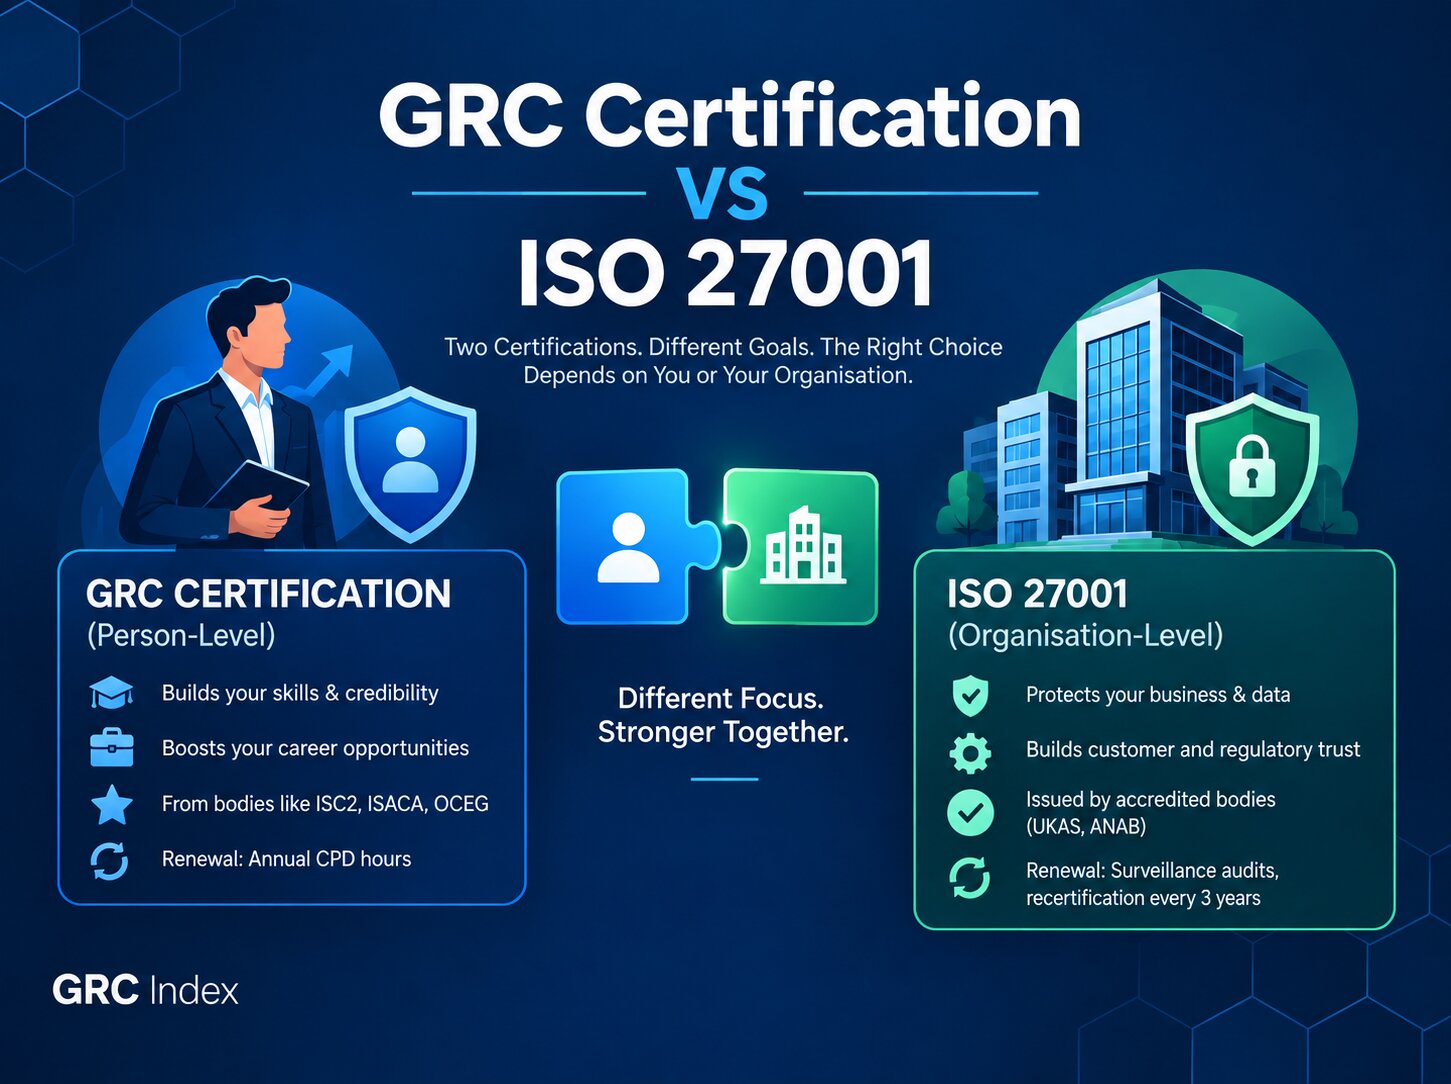
The core difference is simple. ISO 27001 certifies a management system. In SOC 2, the controls that keep a service safe are discussed. ISO 27001 vs SOC 2 therefore comes down to scope, output and region.
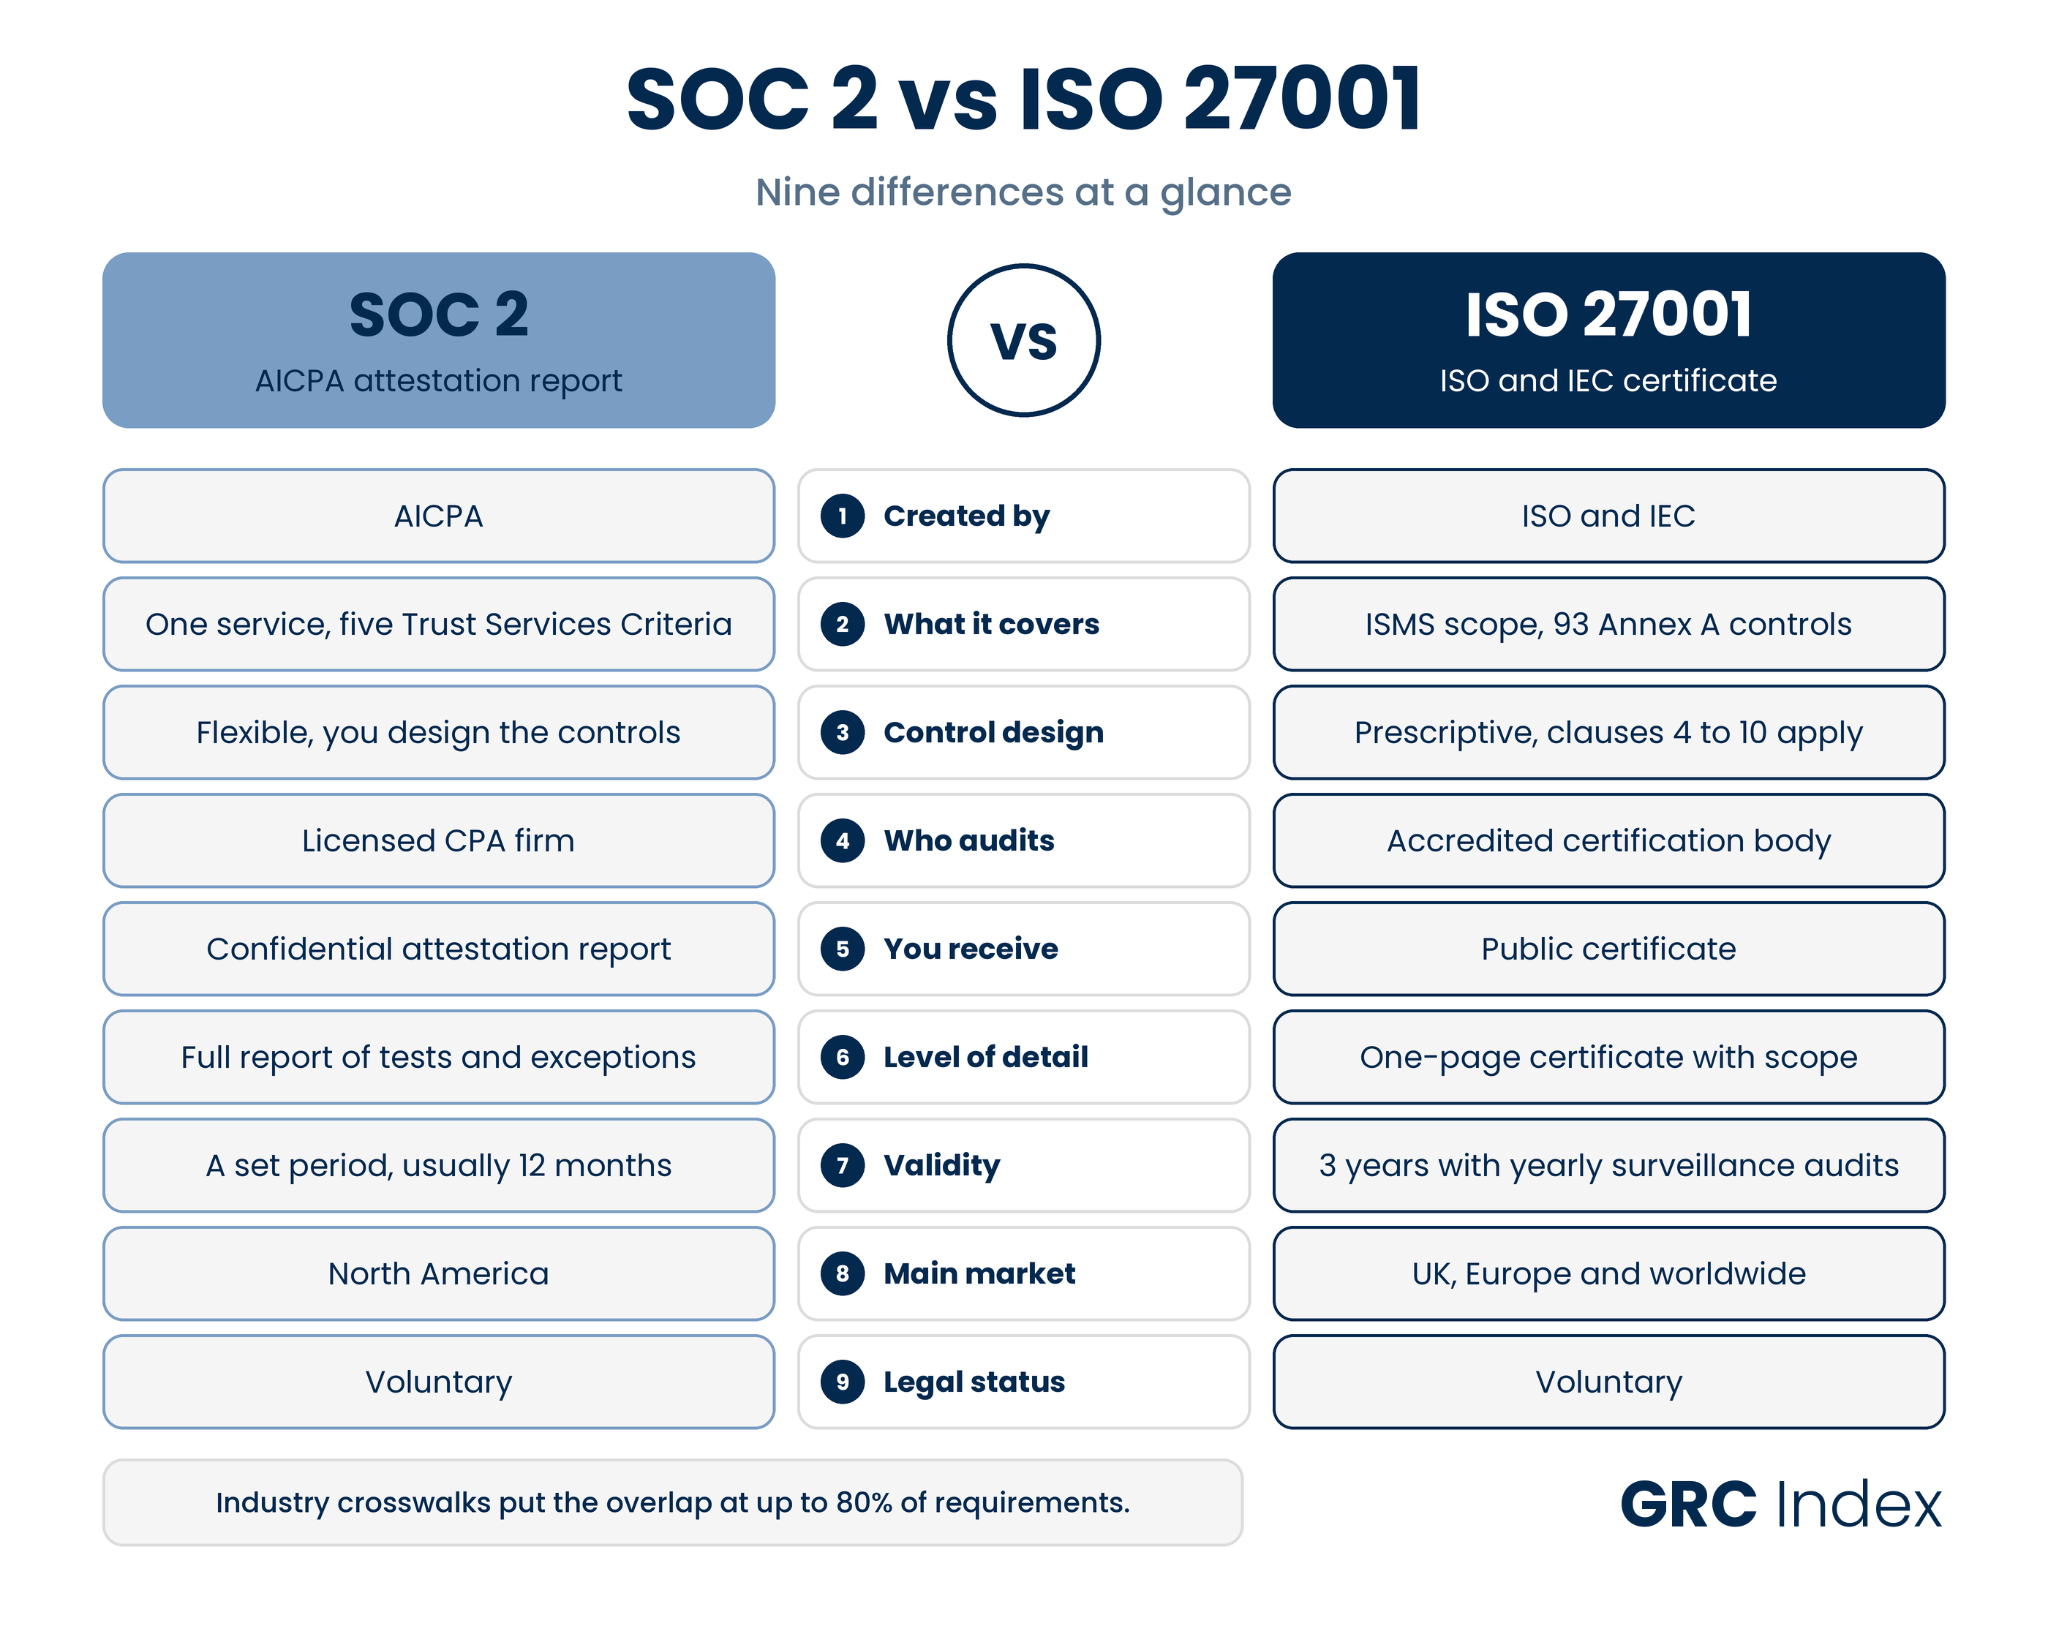
ISO 27001 sets the same clauses for every adopter. It is possible to implement controls that are SOC 2 compliant. Which approach suits your team?
Region matters most for UK and European sales. Most UK and European buyers ask for ISO 27001. On the other hand, there is a large number of US buyers who ask for SOC 2. Industry crosswalks put the overlap at up to 80% of requirements.
There are also differences in effort between ISO 27001 vs SOC 2 compliance. ISO 27001 asks you to run a living management system. On the other hand, SOC 2 asks you to prove that chosen controls work over time. Work for one standard therefore supports the other.
Who Audits You and What You Receive
ISO 27001 uses an accredited certification body. UKAS is the country's main organization for accrediting businesses. The body audits you in two stages. A pass earns a three-year certificate.
An auditor returns every year for a surveillance audit. A full recertification audit follows in year three. Scope decides what the certificate proves. A certificate that covers one office says nothing about your other sites.
A SOC 2 audit is conducted, and an opinion is written by a certified CPA company such as grci.net. The report covers a set period, often 12 months. You need a new report each year to keep your proof current. A bridge letter can cover the gap between two reports.
Most businesses in the UK and Europe have to deal with an extra point. An AICPA SOC 2 attestation must come from a licensed CPA firm. Some European accountancy firms issue ISAE 3000 reports against the same criteria. Everyone who buys something should be asked which report they agree with.
The Road to Compliance: How Long Each Takes
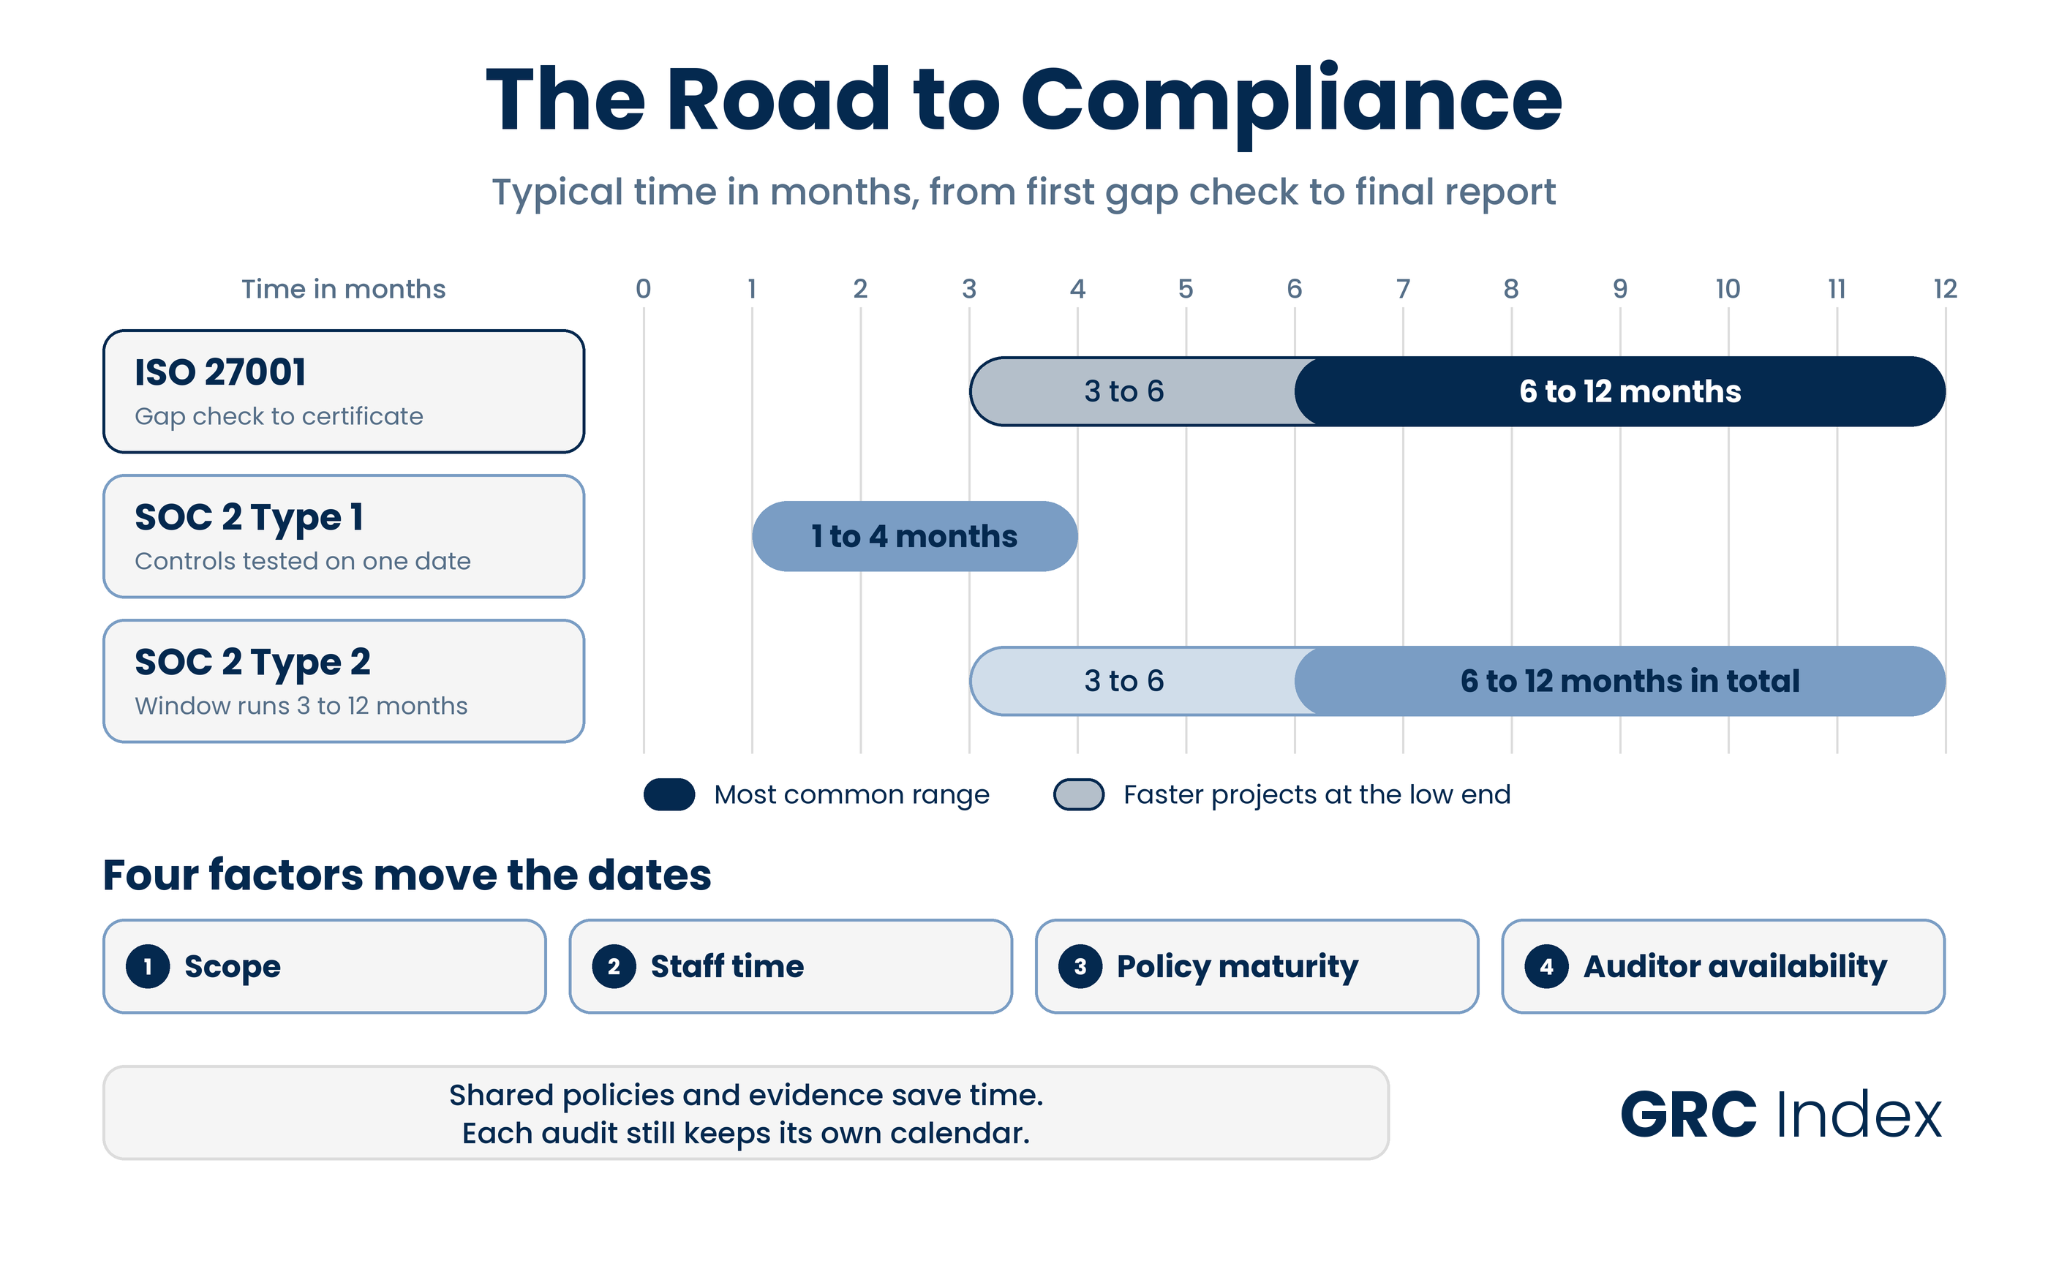
ISO 27001 projects run from three to twelve months. Six to twelve months is the most common figure. A small firm with clear policies moves faster. A multi-site firm often needs the full year. SOC 2 follows two clocks. A Type 1 report can take one to four months. A Type 2 report adds an observation window of three to twelve months. Many firms need six to twelve months in total for a first Type 2 report.
Four factors move the dates. They are scope, staff time, policy maturity and auditor availability. Which one would slow your team most? You should plan for overlap if you pursue both. Shared policies and evidence save time. Each audit still keeps its own calendar.
From Gap Analysis to Final Report: The Certification Steps
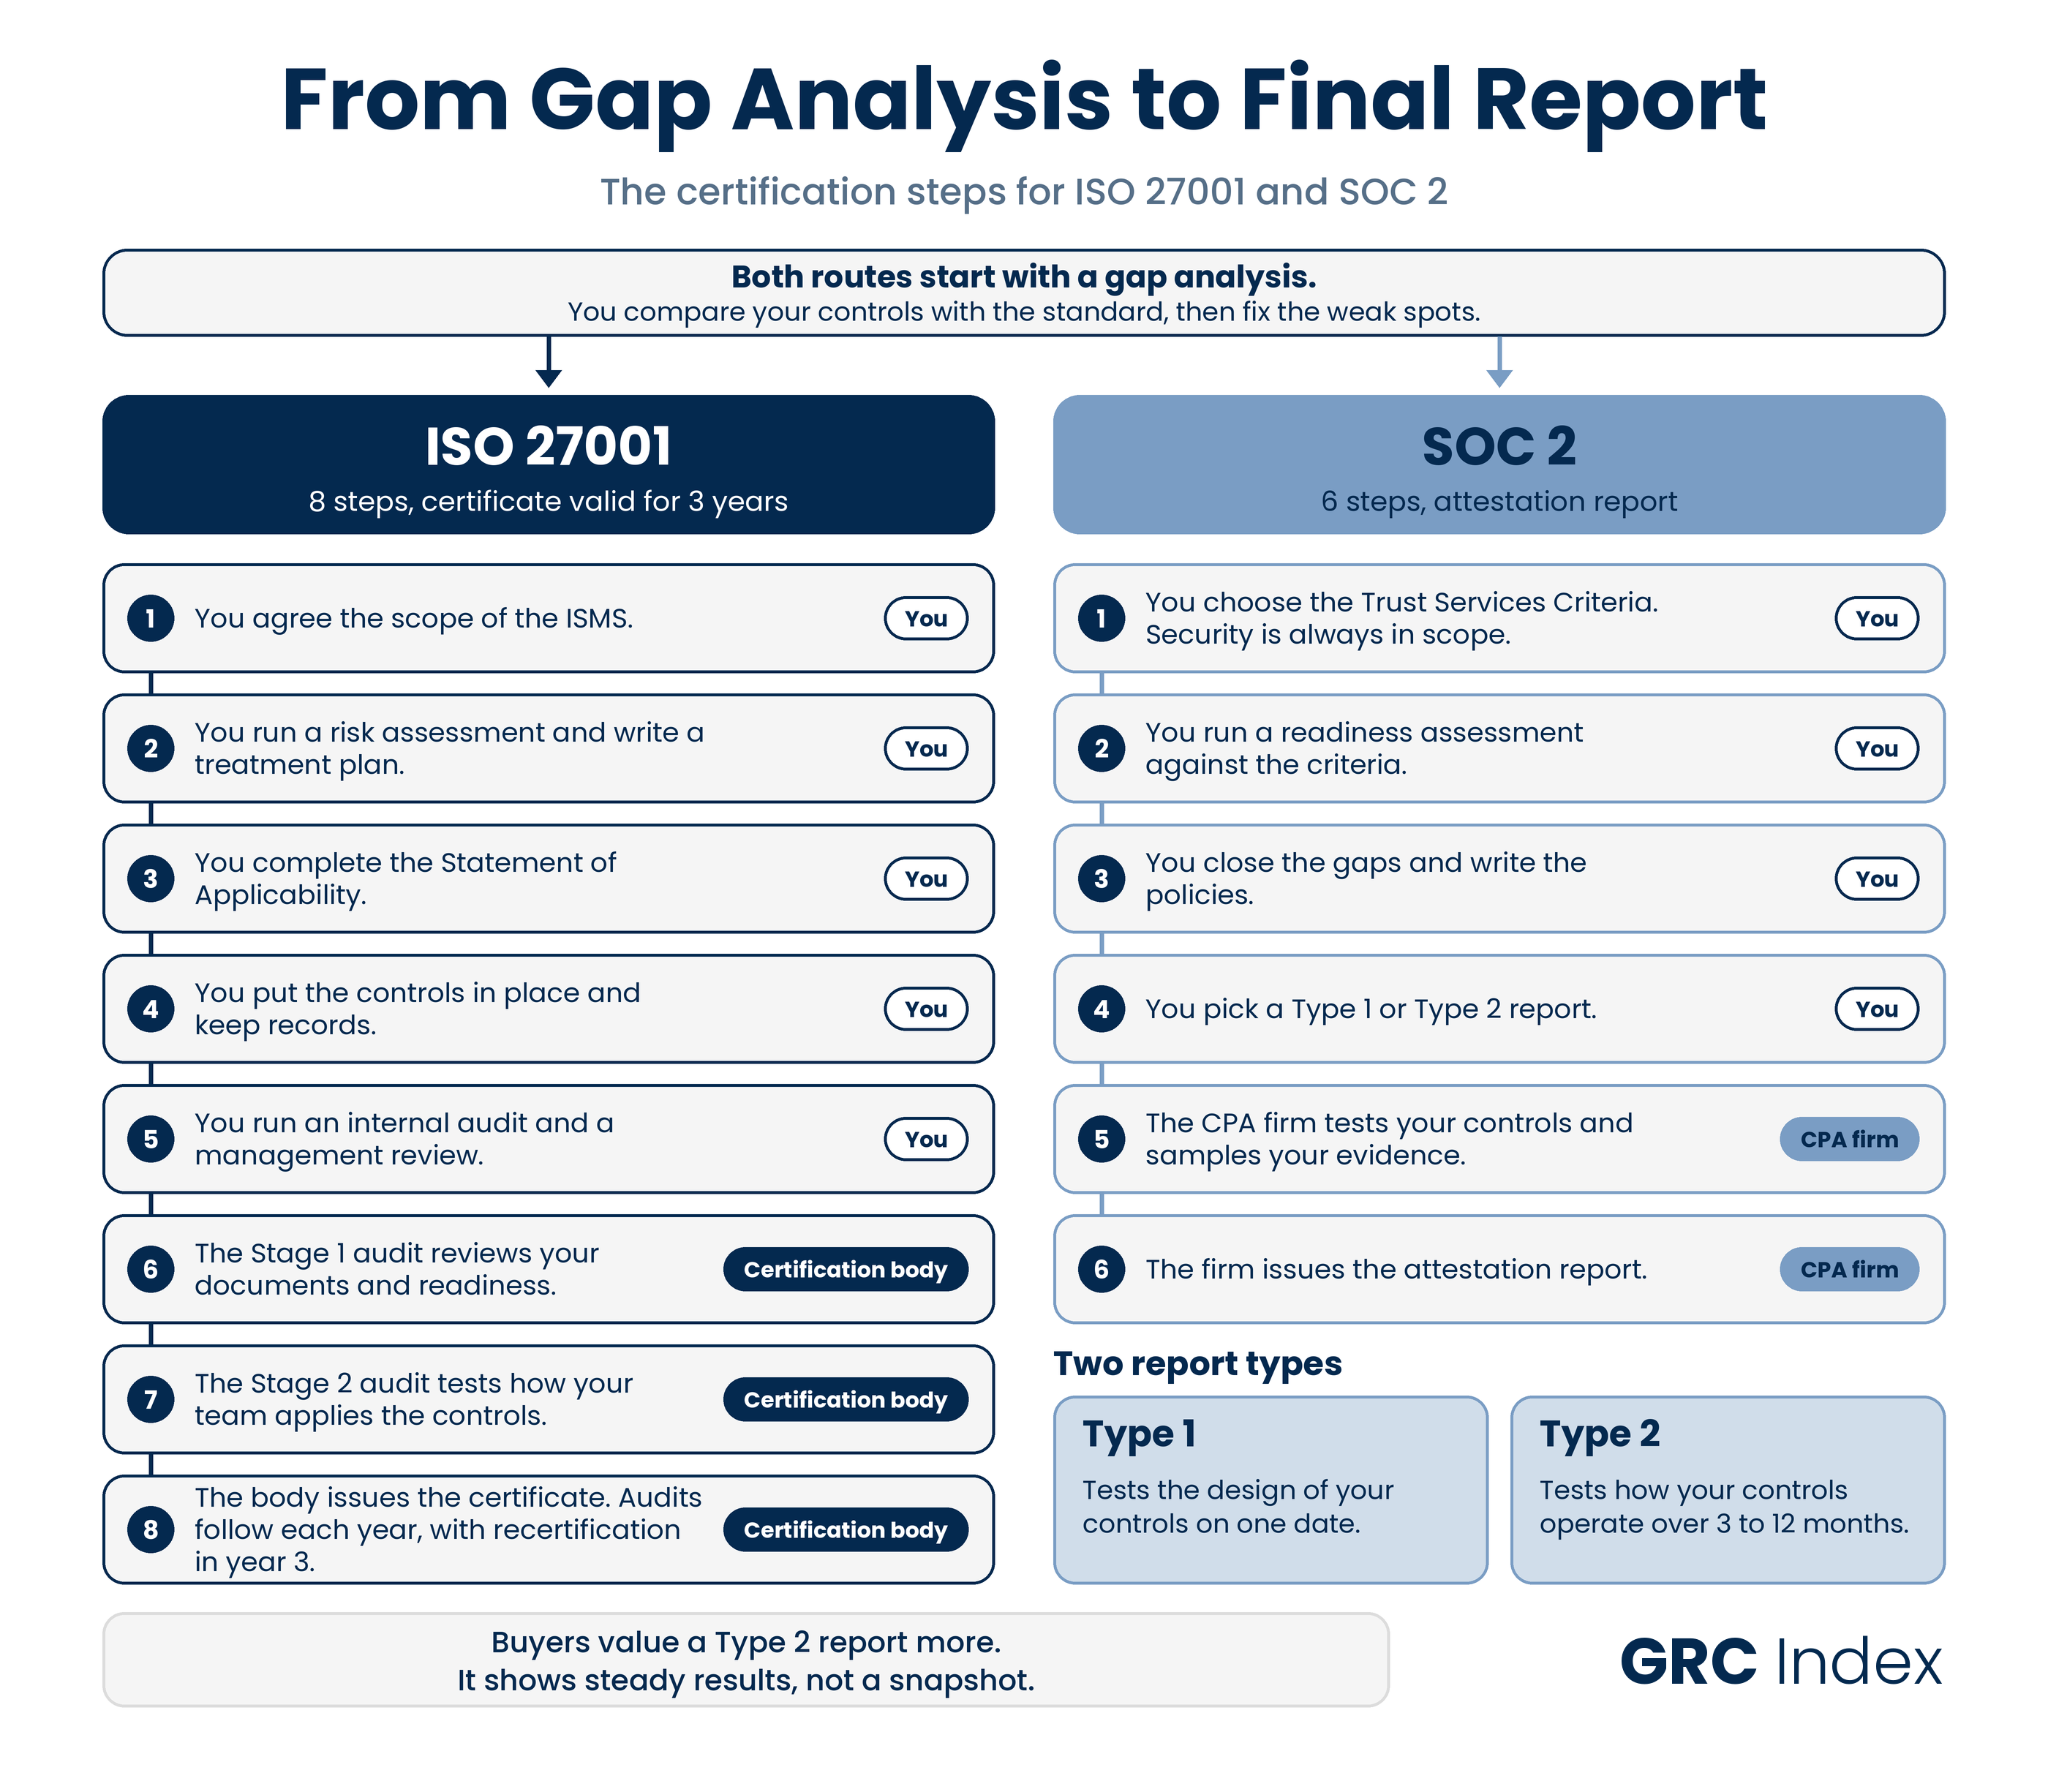
Both routes start with a gap analysis. You compare your controls with the standard. You then fix the weak spots.
ISO 27001 Steps
- You agree the scope of the ISMS.
- You run a risk assessment and write a treatment plan.
- You complete the Statement of Applicability.
- You put the controls in place and keep records.
- You run an internal audit and a management review.
- The certification body runs the Stage 1 audit to review your documents and readiness.
- The Stage 2 audit tests whether your team follows the controls.
- The body issues the certificate. Surveillance audits follow each year, and a recertification audit follows in year three.
SOC 2 Types and Steps
SOC 2 has two report types.
- A Type 1 report tests the design of your controls on one date
- A Type 2 report tests how your controls operate over three to twelve months
Buyers value a Type 2 report more. It shows steady results, not a snapshot.
- You choose the Trust Services Criteria. Security is always in scope.
- You run a readiness assessment against the criteria.
- You close the gaps and write the policies.
- You pick a Type 1 or Type 2 report.
- The CPA firm tests your controls and samples your evidence.
- The firm issues the attestation report.
The Documents Auditors Ask to See
Auditors work from evidence. The two standards ask for different records. You should prepare these dcoument early before the audit. Which records could your team produce today?
ISO 27001 Records
- Scope of the ISMS
- Information security policy
- Risk assessment and risk treatment process
- Risk assessment and treatment results
- Statement of Applicability
- Security objectives
- Evidence of staff competence
- Internal audit records
- Management review minutes
- Records of corrective action
SOC 2 Records
- System description
- Management assertion
- Policies and procedures
- Risk assessment
- Access review records
- Change management records
- Incident logs and response records
- Vendor review records
- Staff onboarding and awareness records
The Statement of Applicability matters most for ISO 27001. It lists all 93 Annex A controls and explains each choice. SOC 2 auditors sample your evidence across the full period. A skipped access review can become an exception in your report.
Common Myths That Cloud the Decision
Myth 1. ISO 27001 replaces SOC 2. Buyers rarely accept one in place of the other. A US buyer that asks for SOC 2 will not treat an ISO 27001 certificate as equal. The same holds in reverse.
Myth 2. SOC 2 is a certificate. SOC 2 is an attestation report. A CPA firm gives an opinion on your controls. Nobody certifies you.
Myth 3. SOC 2 is the easy option. Flexibility is not the same as ease. A Type 2 audit needs months of steady evidence. You also design your own controls. That takes skill.
Myth 4. ISO 27001 suits only large firms. The standard scales to your size. A small firm sets a narrow scope and picks the controls that fit its risks. A tight scope also keeps the audit short.
Myth 5. A certificate or report proves you are safe. Neither one proves that you will never face an incident. Both prove that you manage risk in a checked way. Your controls still need daily care.
Which One Suits Your Business?
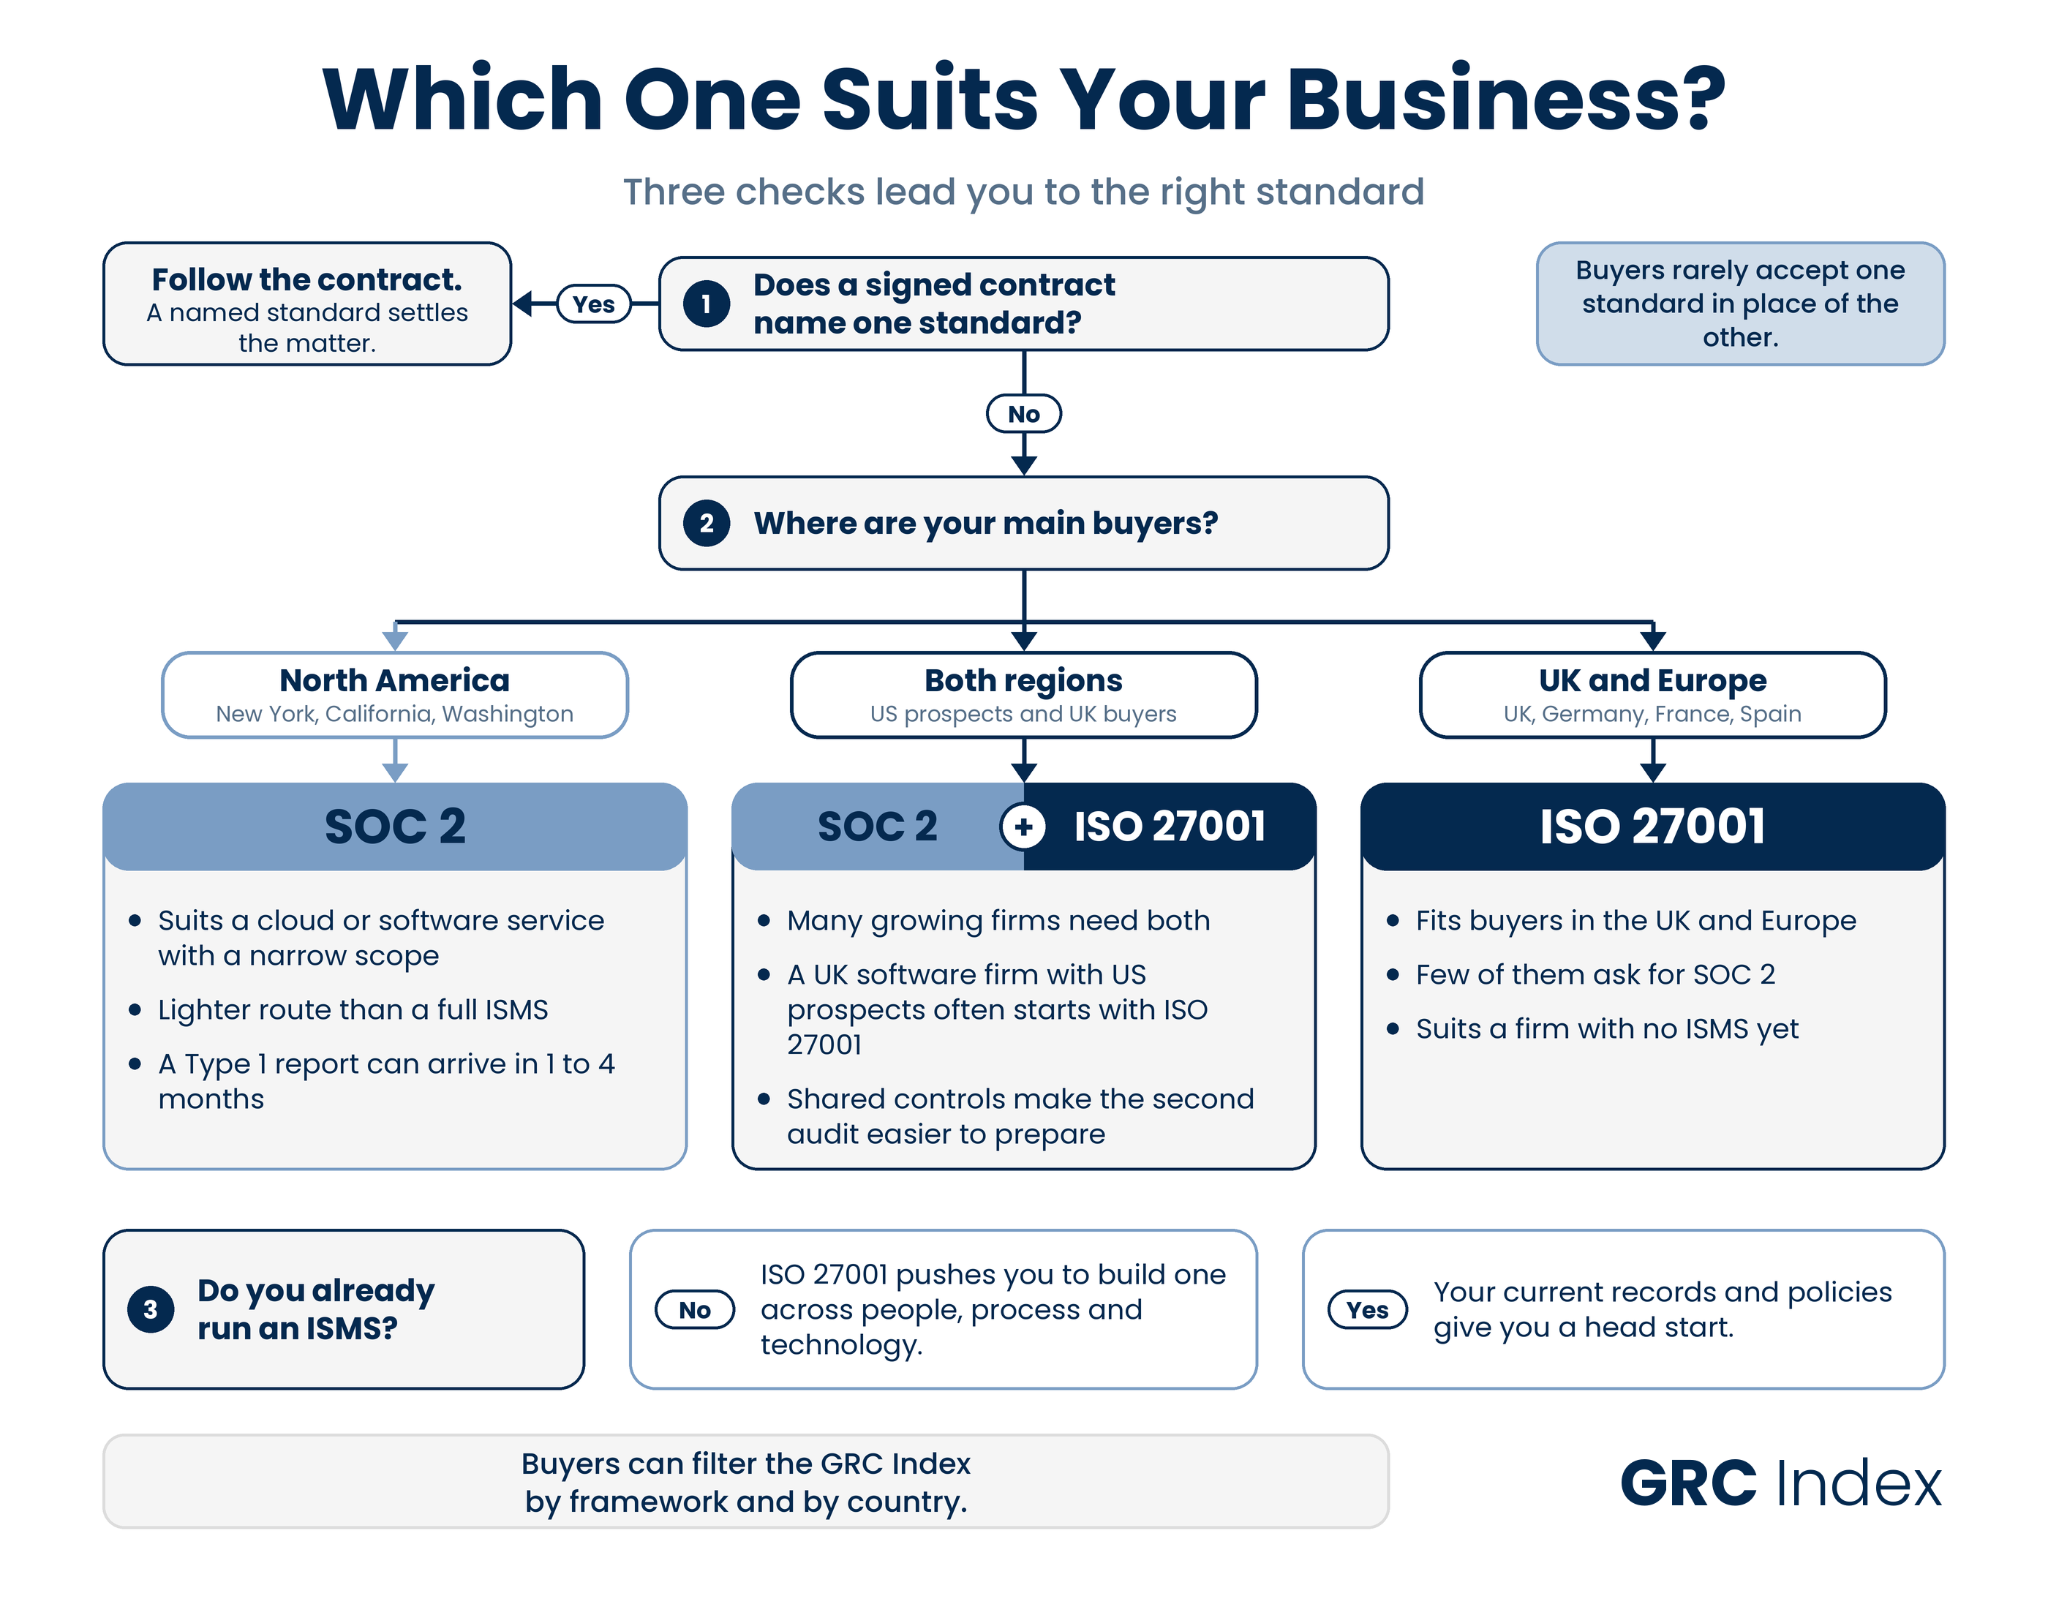
The best choice depends on your buyers. You should ask three questions first to yourself. Where are your customers, what do their contracts name and do you already run an ISMS?
A signed contract that names one standard settles the matter. According to Europ rules such as NIS2 and DORA, buyers are being pushed toward closer supplier checks. You can also check the NIS2 and GRC guide, which explains what the directive means for your organisation.
When SOC 2 Is Better
SOC 2 is the better pick when your main buyers are in North America, like New York, California, Washington, and more. It also suits a cloud or software service with a narrow scope. The route is lighter than a full ISMS. A Type 1 report can arrive in one to four months.
When ISO 27001 Is Better
ISO 27001 is the best choice when your buyers are in the United Kingdom (UK) or Europe like Germany, France, Spain, and more. A few of them ask for SOC 2. It also suits a firm with no ISMS yet. The standard pushes you to build one across people, processes, or technology.
Many growing firms need both. A UK software firm with US prospects often starts with ISO 27001 and adds SOC 2 later. Shared controls make the second audit easier to prepare. A decision tree shows the path at a glance.
Buyers also look for proof before they sign. The GRC Index is the best platform where you can list your organisation and lets them filter organisations by framework, such as ISO27001 and SOC2, and by country. Your own entry can show your status in one place. Which proof would your next buyer ask for first?
Frequently Asked Questions
Is SOC 2 Legally Required?
No, SOC 2 is not required by any law or rule made by the government. Buyers ask for it in contracts. UK GDPR and EU GDPR require appropriate security measures.
Is ISO 27001 Equal to SOC 2?
No. ISO 27001 certifies a management system. SOC 2 reports on the controls that protect a service. Most buyers do not accept one in place of the other. The two overlap heavily. Work for one helps the other.
Is it hard to get SOC 2 certification?
Somewhat difficult, getting a SOC 2 report (also known as a "certification") depends on how mature your company's security is now, the size of your team, and the compliance automation tools you use.
Why Is SOC 2 So Expensive?
Service Organization Control 2 (SOC 2) is expensive because it's not just a license fee; it's an in-depth, multi-layered audit of security and operations done by a third party. Accountants who are certified by the government
How Long Is SOC 2 Valid?
A SOC 2 report is valid for 12 months from the conclusion of the audit or observation period (depending on the type of report, this may be the date of issue).
How Long Is ISO 27001 Valid?
The ISO 27001 certificate has validity for three years after it is given out.
Can You Get Both at the Same Time?
Yes, you can work toward and get both ISO 27001 certification and SOC 2 attestation report at the same time. In fact, doing them at the same time is often faster than doing each one separately.