The American Institute of Certified Public Accountants (AICPA) created SOC 2. It launched the SOC reports in the early 2010s. The AICPA set the current rulebook, the Trust Services Criteria, in 2017. It then updated the points of focus in 2022. SOC 2 is not a legal rule. Still, big buyers often write it into their contracts. A-LIGN, an audit firm, adds that a report can often replace a 500-question security survey. SOC 2 began in the US. However, A-LIGN says global buyers accept it more each year. That matters if you sell software from the UK or Europe to US clients.
First, you need written policies and controls that work. Next, you hire a licensed CPA firm, because only those firms can run the audit. Once the audit is complete, the auditor will provide a report that is valid for about one year. Type I and Type II are the two varieties of SOC 2 that are available. Within a single day, your controls are examined by a Type 1 report. A Type 2 report tests them over many months. In this article, we will explain SOC2 types, their difference, and their benefits. In this blog, we can cover every single which you need to know about SOC 2.
What Is SOC 2 Type 1?
Within a SOC 2 Type 1 report, your controls are evaluated on a single date that is predetermined. It's kind of like a picture of your protection system. The auditor wants to know if your controls are well-thought-out enough to meet the requirements. The auditor doesn't check how well the controls keep working over time. If you want a Type 1 report, you can receive it more quickly and for less money. A-LIGN says the audit usually takes two to four weeks. Putting your controls in place is still the first thing you need to do. It is possible that the preparation work will take up to six months to complete.
New businesses often need that. So do firms that changed their systems lately. A deal that must close fast can also point you that way. A ten-person start-up in Manchester might need to win a US client next month. A Type 1 report can give it proof in weeks. However, some buyers now turn Type 1 reports down. You should ask your buyer before you commit.
What Is SOC 2 Type 2?
This is an independent audit that looks at how well an organization's security controls worked over a certain amount of time (usually 3 to 12 months). The following is an example of what a SOC 2 Type 2 report looks like. For instance, the auditor may check that you removed access for staff who left. The final report lists each result and any exceptions.
Type 2 takes longer, and it can cost more than Type 1. A-LIGN says most audit periods last six to twelve months. Many organisations start with a three-month window and move to twelve later. A longer window shows buyers stronger habits. SaaS firms, cloud providers and finance firms usually do. Some experts say you should skip Type 1 and go straight to Type 2. They point out that you then pay for one audit and not two.
What Sets SOC 2 Type 1 and Type 2 Apart?
The main differences between SOC 2 Type 1 and Type 2 reports are the amount of time they cover, the things they test, and the level of assurance they give to customers. The AICPA Trust Services Criteria are used by both to judge a company's internal controls. These are privacy, processing integrity, availability, security, and processing integrity.
The fee ranges come from US CPA firm The Pun Group. You should treat them as a guide only. Your own quote will depend on your scope and your auditor.
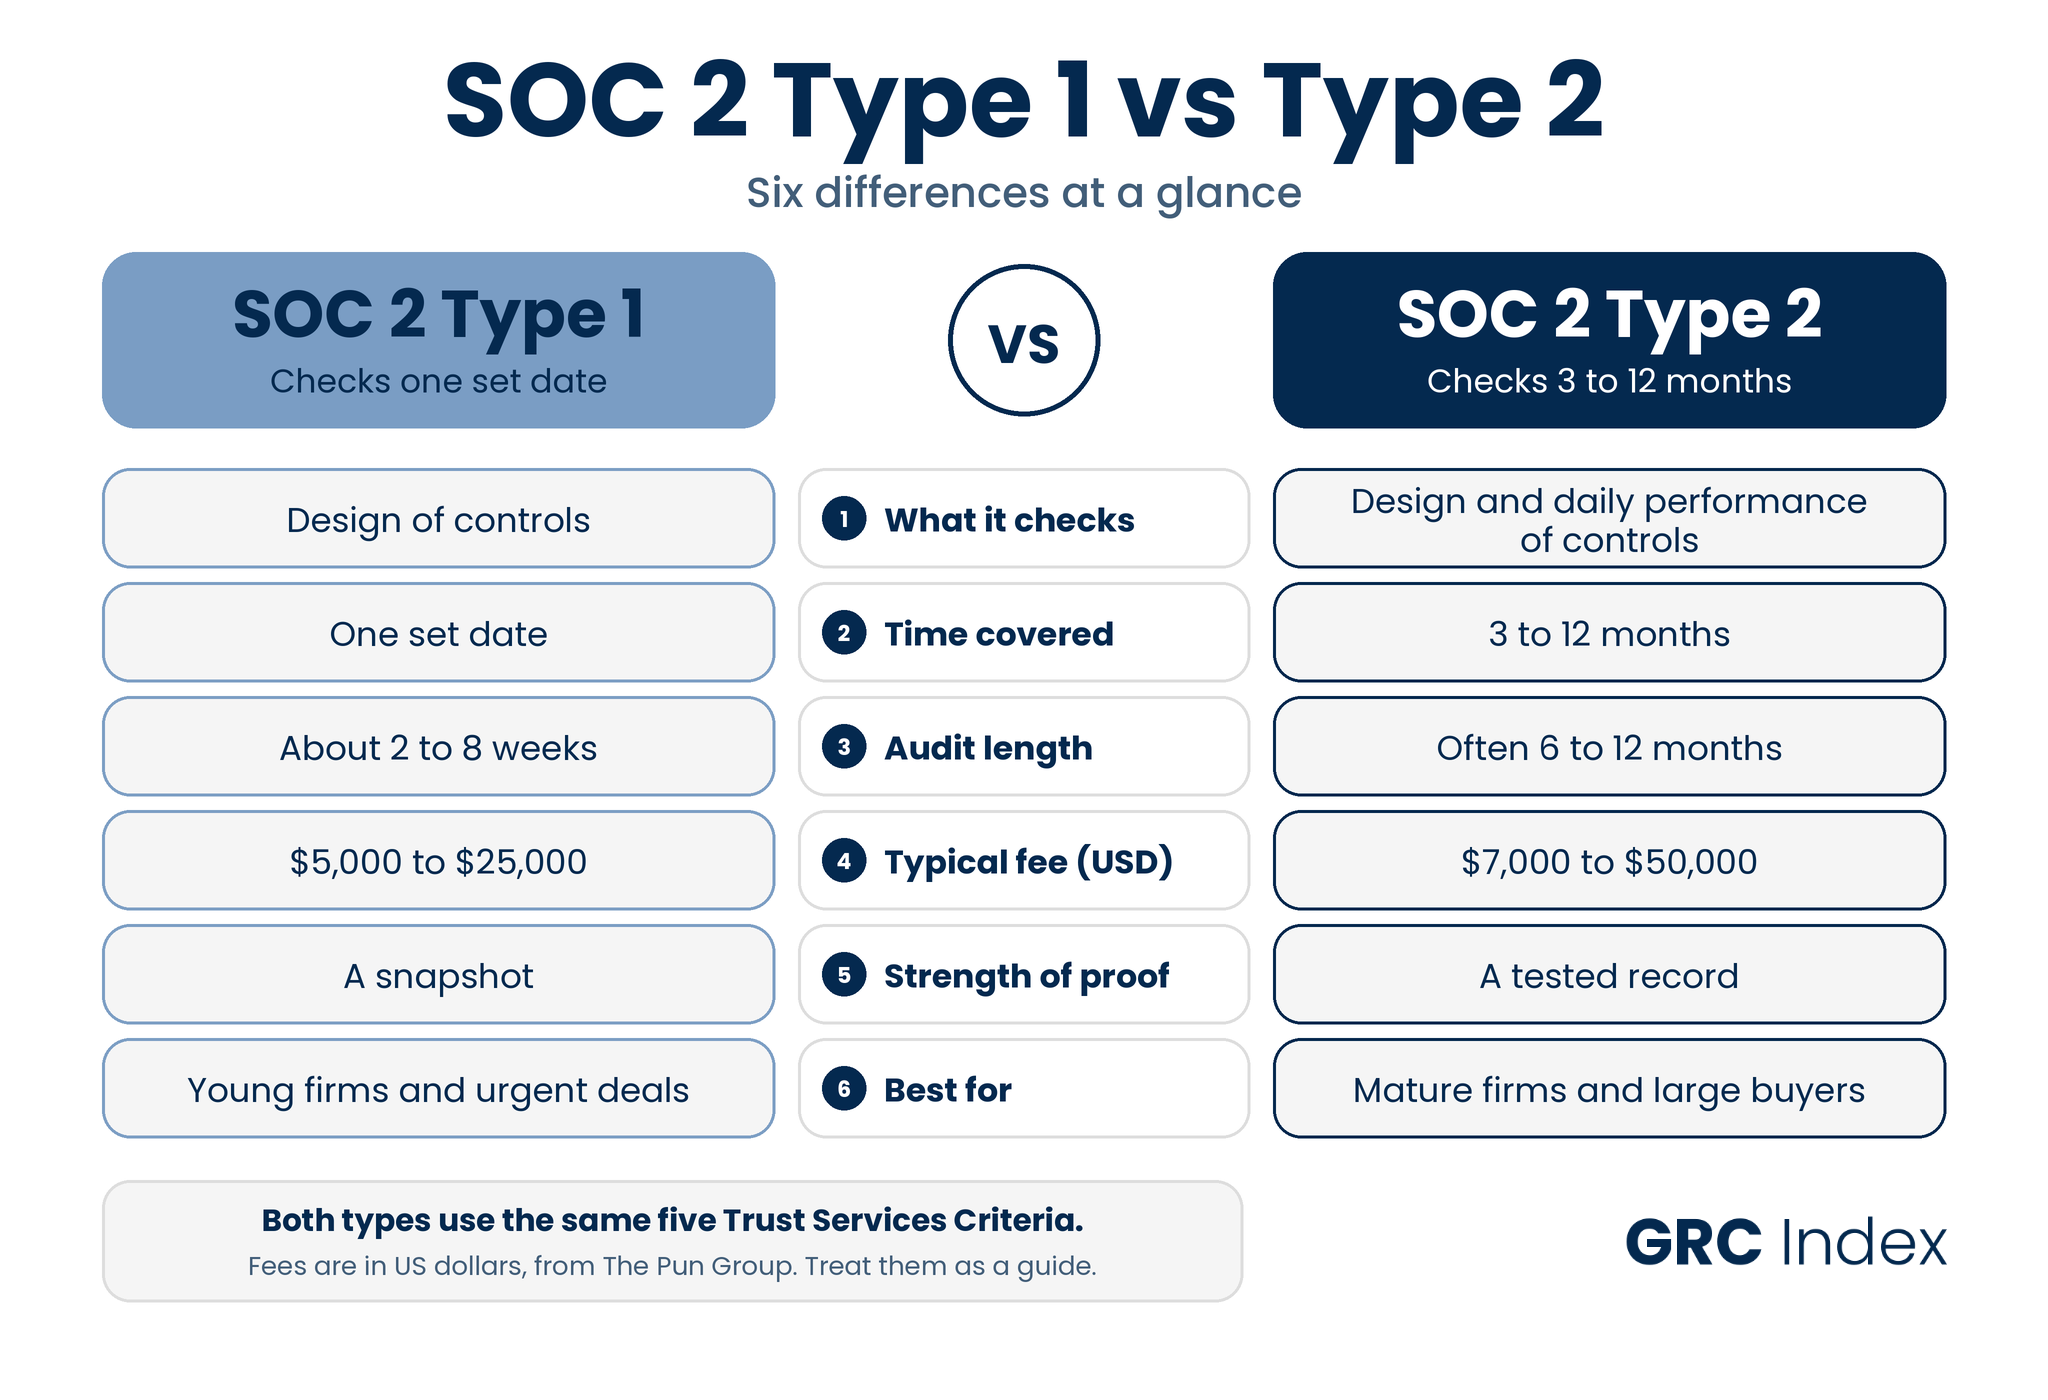
Type 1 checks one date. Type 2 checks the full window.
Three questions can guide you. How fast do you need proof? How strong must that proof be?
You should pick Type 1 when speed matters most. You should pick Type 2 when buyers want proof that lasts. Many firms do both in order. They take Type 1 first and Type 2 later. Do UK and European buyers ask for more than SOC 2? Many also ask for ISO/IEC 27001. ISO's 2022 survey counted over 70,000 certificates in 150 countries. An ISO certificate lasts three years with yearly checks, A-LIGN says.
How to Automate SOC 2 Compliance
Compliance software can cut much of the routine work. It links to your cloud tools and collects proof for you. It also flags gaps and keeps a task list. A-LIGN lists readiness checks, evidence collection, policy templates and cloud links as key features.
Software does not replace the auditor. Only a licensed CPA firm can issue the report. The AICPA's SOC page also carries articles that question "fast and easy" SOC promises. So you should check that your auditor holds a CPA licence.
A clear order keeps the work calm. A common path looks like this:
- A readiness check that finds your gaps
- Fixes and written policies
- Tool links that collect proof
- A CPA firm that you choose
- The audit, then the report under NDA
You can start with the free self-assessment, which scores your governance, risk and compliance against ISO 27001, SOC 2 and COSO. The GRC Index already lists over 1,100 organisations. Your team can also build skills through GRC courses and certification.
FAQ’s
Is SOC 2 better than ISO 27001?
There is no one "better" structure; they are all different and serve different markets, goals, and ways of judging. The best one for you will rely on where your customers are and what kind of proof they want.
Is there a SOC 3?
Yes, SOC 3 is a genuine, publicly available compliance report.
Why is SOC 2 so expensive?
The total cost of SOC 2 is expensive because it includes more than just a fee. It includes fees for an independent CPA audit, time spent on deep internal engineering, required security tools, and ongoing monitoring.
Is it hard to get SOC 2 certification?
It can be relatively to very hard to become SOC 2 compliant, based on how secure your company is already, how many systems you have, and whether you choose Type 1 or Type 2.